Posts

NotPetya: Good Practices Final Exam

June 27, 2017, 9:45am Petya has struck and InfoSec Twitter is in full crisis mode. Petya appears to be very sophisticated and I have heard many exploits given for it's methods of spreading and I'm going to touch on each one. I am not here to prove that each one of these things is true about Petya but just going over how each one of these things can be prevented in the future. Update, June 27, 2017, 10:10am:  It is now being called NotPetya by Kapersky who decided it is unrelated. Either way this stuff still applies.  CVE-2017-0199 I have heard that it is using CVE-2017-0199, which I wrote about here , as an initial entry to networks via email. This has been mentioned once or twice. It bypasses macros in Microsoft Office, but there are patches available and my notes show how to break code execution if you're really paranoid. Update : Loki, a different ransomware, might be using CVE-2017-0199 and not Petya. Even still... Update, June 27, 2017, 10:30am:  Petya/...

Windows Management Interface (WMI) Filtering for Group Policy Objects

During my recent work with a local law firm overhauling their network and designing a new Active Directory (AD) domain structure I have learned some tricks. One is WMI Filtering for applying an entire Group Policy Object (GPO). Windows Management Interface (WMI) Filtering is a feature in the Group Policy Management Console (GPMC) on Windows Server operating systems that let you create conditional logic as to whether or not a GPO applies to a specific computer within it's assigned Operational Unit (OU). Here's an example filter taken from the Security Baseline for Windows 10 (Draft) : Internet Explorer 11.mof instance of MSFT_SomFilter { Author = "Administrator@JST4KXS.local"; ChangeDate = "20131215210840.077000-000"; CreationDate = "20131031204931.789000-000"; Description = "Applies Internet Explorer 11 Settings"; Domain = "JST4KXS.local"; ID = "{F78EB5A2-B8C0-49FC-BB29-86DD2D3E0B15}"; ...

On "Gaming" Social Media

Image
I begin this blog post with an acknowledgment of the irony of the situation. But I'm taking the opportunity use this chance to highlight the social media snowball and how to use your momentum responsibly. This post is in no way an indictment of MalwareTechBlog, nor am I implying that they did anything wrong here . If I come across as petty it is intentional and not sincere. On May 26th, 2017, I tweeted about a bug with Microsoft Office in which a background task would flicker a command prompt briefly due to it being mistakenly registered as a user-context task. First! Thirty-seven hours later the Savior of the Internet, Slayer of Wcry, MalwareTechBlog posted a tweet that said basically the same thing . With no significant additional information. Second, more popular mouse gets the cheese Social media is all about visibility. After MalwareTech posted their tweet SwiftonSecurity retweeted it, and between both of their substantial platforms a very visible conversation ...

Securing a Law Firm, part 1: Securing Chrome

Image
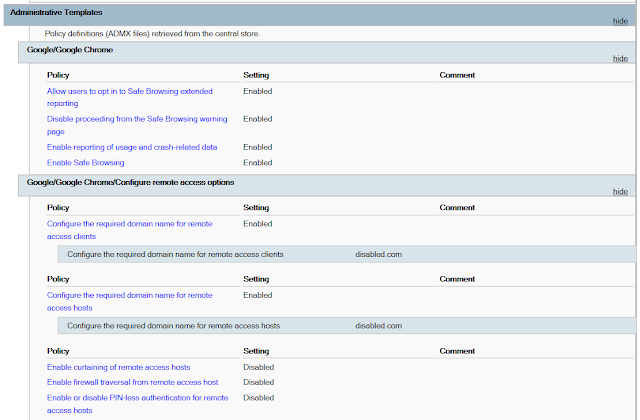
On a snowy day, late in December of 2016 I sat in a corner office of a local law firm with the firm's IT manager discussing the hottest topic of the week - ransomware. After a law firm down the road had been hit by a ransomware attack the partners were afraid. They were asking a lot of questions for which the IT manager had serviceable answers. I had my own questions in preparation for my practicum beginning in the new year. Scribbled in various notebooks and loose scraps of paper in my bag laid the anatomy of the day's typical ransomware attack. My previous months had been spent picking up the tools of the infosec trade from the sidelines of Twitter. I wanted to see how much of it I could use. Over lunch I probed the IT Manager about their threat model, what they were prepared for, and their recovery plans for when they failed. I approached them because I knew their environment wasn't prepared for a modern attack. My goal during the meeting was to see just how bad...

Introduction and Ethics

1. Don't hurt others 2. Protect those who cannot protect themselves 3. Strive to be better My name is ephemeral. I currently go by Amanda on Twitter , and by NotAwful in most other places. It will change in the future but for now I am comfortable and have no plans to change that. As of writing, I am a networking and telecom student studying information security on the side. I do not have much real-world experience but I am seeking it avidly and learning as much as I can until I get there. My primary interest in infosec is malware research and software reverse engineering, but before I get there I will likely be working within the realms of general IT. Expect me to post reviews and thoughts about things that I am learning in technology here. I have played a lot of tabletop roleplaying games such as Dungeons & Dragons, Dungeon World, Shadowrun, and a few others. I have also played many video games. I think critically about game design and while you won't see me break...